Enterprise Network Security & Infrastructure Modernization
Secure, resilient, and scalable enterprise networking for organizations in Nepal.
Network Security
Infrastructure
Connectivity
Modernization
Secure
Strengthen network security with next-generation firewalls and access control.
Segment
Design VLANs and logical separation for users, servers, CCTV, and guest networks.
Connect
Enable secure site-to-site and remote access with IPsec VPN.
Ensure Continuity
Build resilient connectivity with dual-ISP paths and automatic failover.
Enterprise Network Security for Organizations in Nepal
As a network security consultant in Nepal, I focus on helping organizations assess, design, implement, and modernize secure enterprise networking environments.
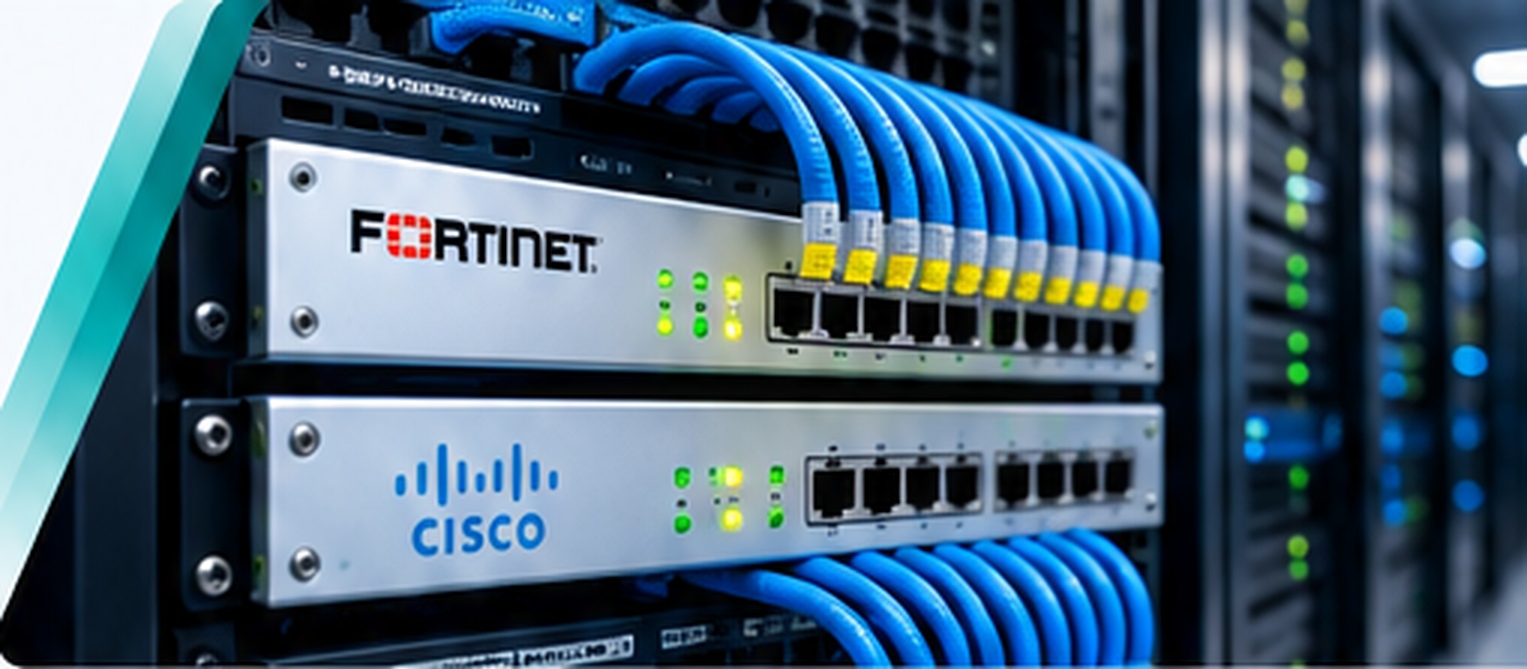
My technical expertise spans Fortinet firewall architecture, Cisco enterprise networking, VLAN segmentation, secure IPsec VPN connectivity, network access control, WAN redundancy, and infrastructure monitoring.
For businesses in Kathmandu, Lalitpur, Bhaktapur, and across Nepal, network modernization requires more than upgrading switches or firewalls. A reliable enterprise network must support critical business applications, protect sensitive information, provide dependable connectivity, and accommodate future growth.
My consulting approach starts with business needs and infrastructure risks, then balances performance, availability, security, supportability, and ongoing operational requirements.
Technical Focus Areas
Firewall Architecture (Fortinet)
Firewall policy design, NAT, application-aware access control, logging, secure management, and high-availability planning.
Enterprise Switching (Cisco)
VLAN segmentation, trunking, routing integration, access-layer design, and switching redundancy.
IPsec VPN & Secure Remote Access
Encrypted site-to-site connectivity and authorized remote access, with appropriate authentication and policies.
Dual-WAN & Network Resilience
Multiple ISPs, link health checks, routing policies, traffic prioritization, and failover validation.
Monitoring & Operational Support
Network health checks, logging, firmware lifecycle, configuration backups, and incident response readiness.
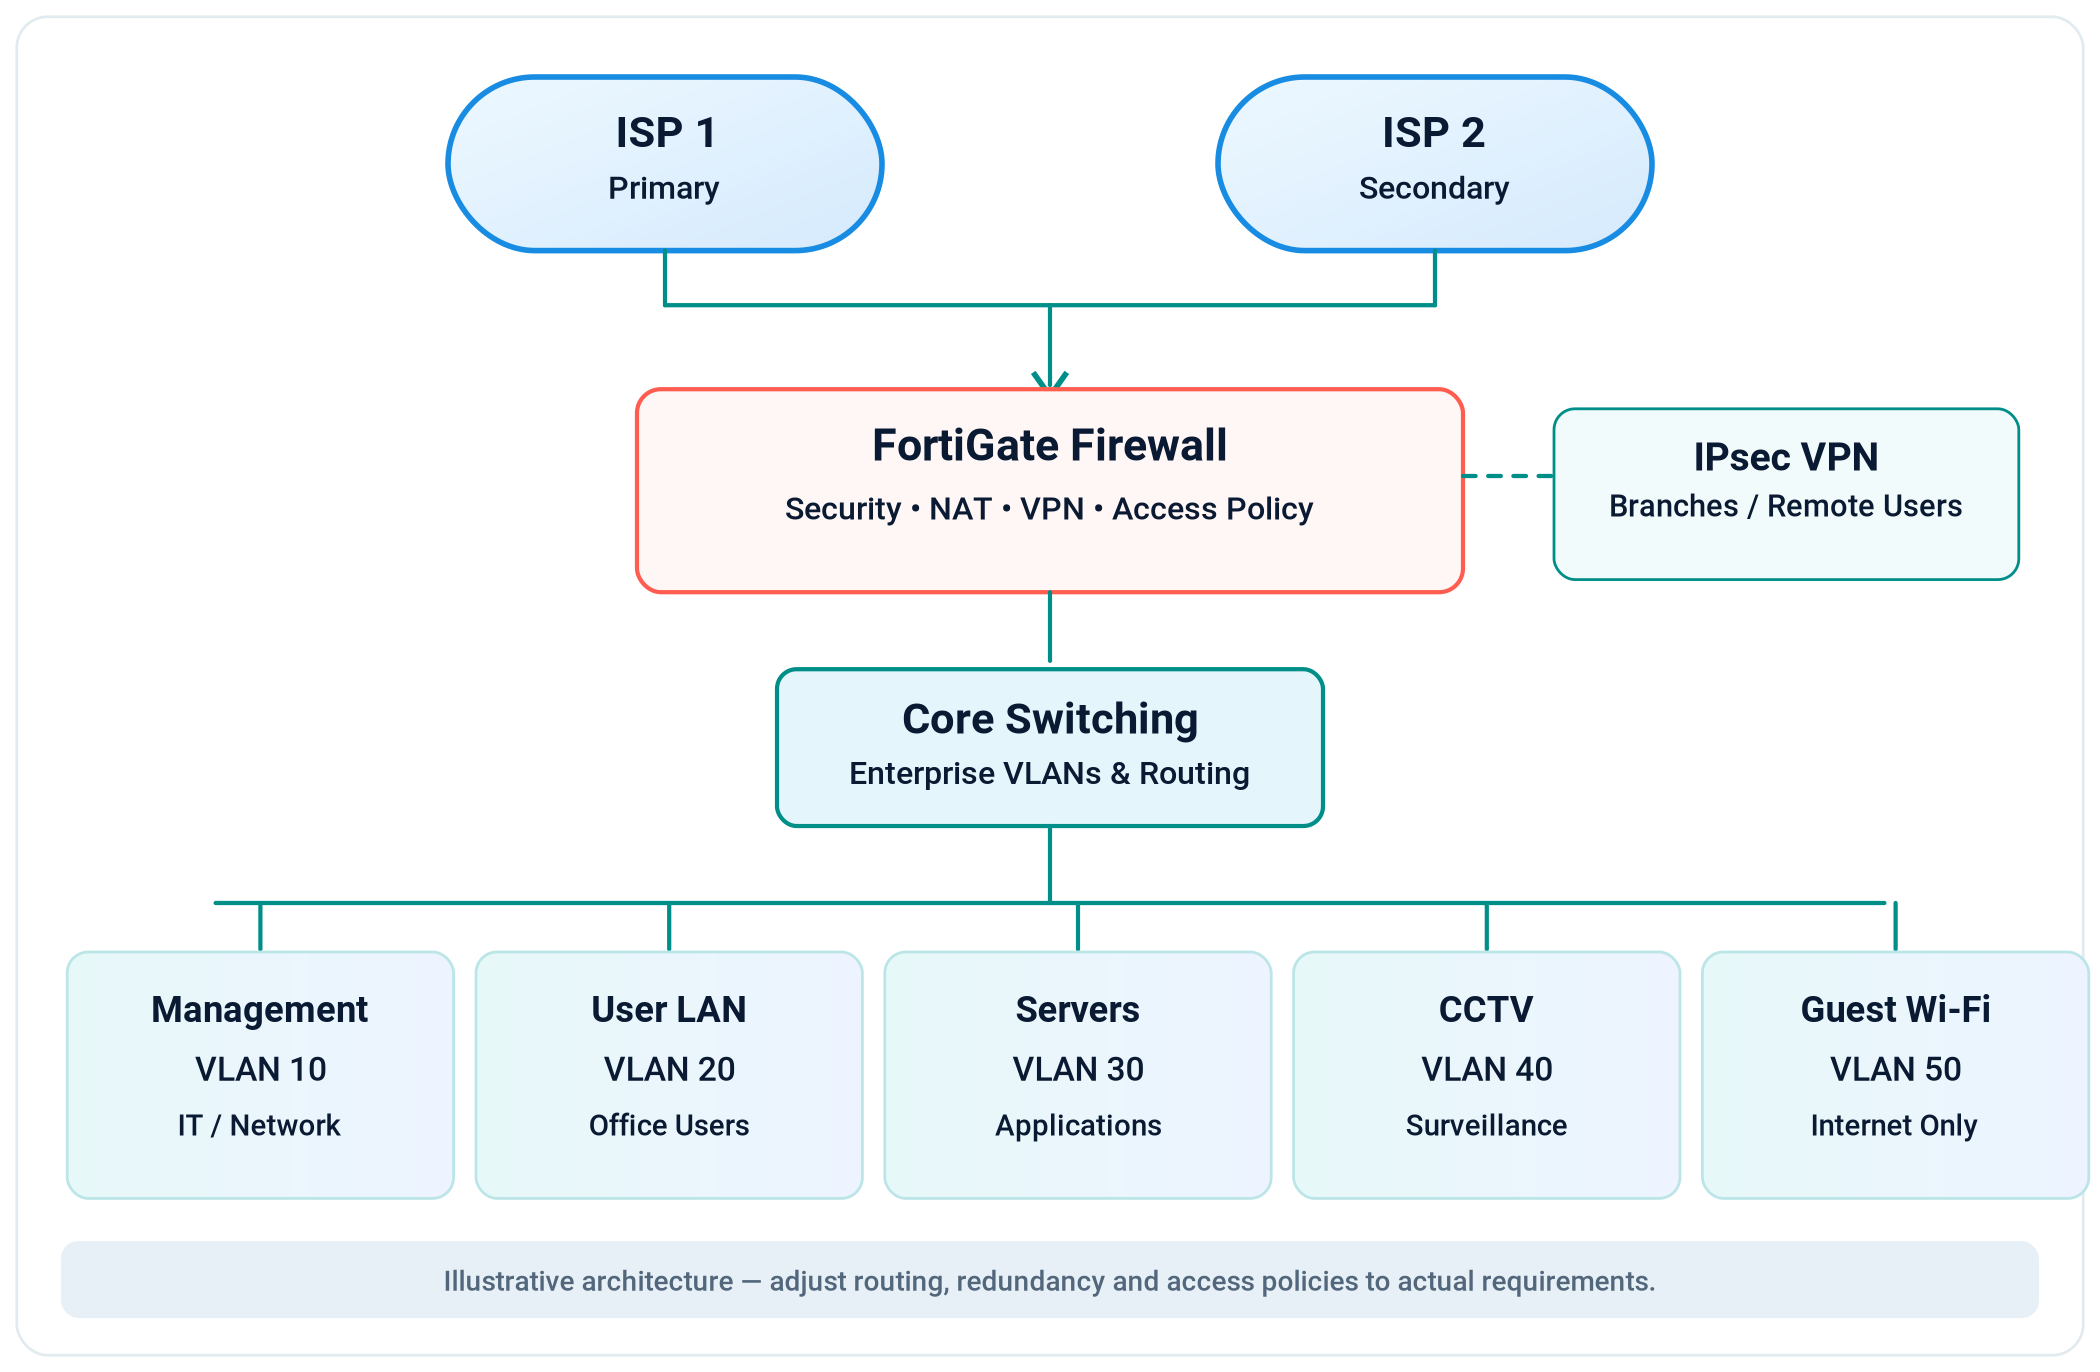
Reference Network Architecture
Conceptual example only. Actual VLANs, routing, connectivity and firewall policies depend on organizational requirements.
Implementation Methodology
1. Assessment
Review the network, security posture, operational dependencies, and business requirements.
2. Design
Develop network, VLAN, firewall, VPN, switching, and WAN designs.
3. Configuration
Configure firewalls, switches, routing, access rules, and monitoring.
4. Migration
Implement controlled changes with configuration backups and rollback planning.
5. Validation
Test connectivity, access controls, VPN, failover, and performance.
6. Handover
Document network design, configurations, procedures, and operational guidance.
Network Security Design Considerations
Infrastructure Redundancy
Design critical links and security components to reduce avoidable disruption.
Least-Privilege Access
Restrict communication to what users, devices, and applications require.
Management Isolation
Use a logically separated, restricted network for administration.
Network Visibility
Monitor performance, events, configuration changes, and device health.
Maintenance & Recovery
Maintain backups, software lifecycle plans, and incident procedures.
Technology Platforms
Frequently Asked Questions
VLAN segmentation creates logical network boundaries. Combined with controlled routing and firewall rules, it can limit unnecessary access between corporate users, servers, management networks, CCTV and guest devices.
A second ISP can provide an alternative connectivity path if one link fails. Effective failover also depends on network health checks, routing behavior, application dependencies and correctly tested policies.
Yes. Fortinet firewalls and Cisco switching infrastructure can be integrated using standard protocols and VLANs. Routing, interfaces, access policies and software compatibility should be validated in the proposed design.
IPsec VPN is appropriate for encrypted connectivity between sites, networks or authorized endpoints. The implementation should account for secure authentication, network routing, least-privilege access, endpoint controls and monitoring.
Discuss Your Network Security Requirements
Planning firewall modernization, VLAN segmentation, VPN connectivity, or resilient enterprise networking in Nepal?
About this technical portfolio: Prepared by Er. Shyam Siwakoti, IT Consultant. This page illustrates an engineering approach rather than measured results from one named customer engagement.
Related expertise: Enterprise Virtualization & Cloud Architecture.